About the author: I hold OSEE and OSCE3, and I work on iOS kernel research for my job. I can barely speak English. This was my second OffensiveCon training, after “Windows Internals for Security Engineers” in 2024.
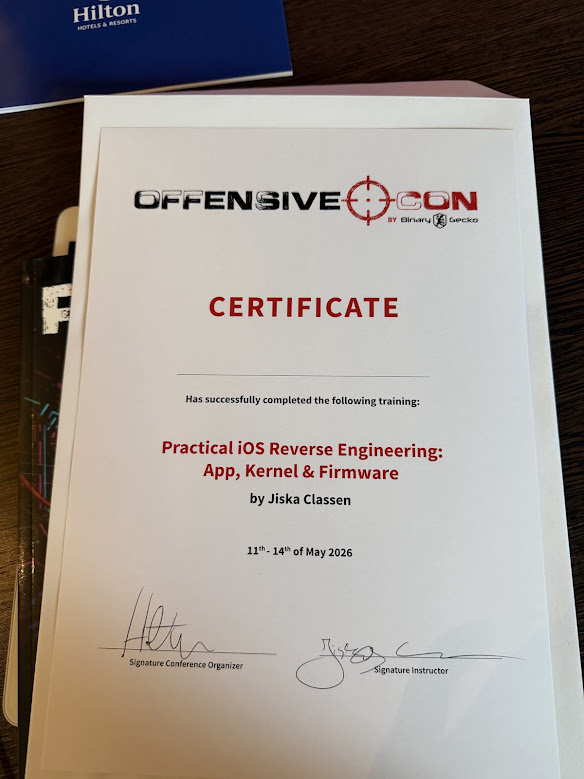
From May 11–14, 2026, I attended “Practical iOS Reverse Engineering: App, Kernel & Firmware”, a training at OffensiveCon 2026, held at the Hilton Berlin. The instructor was Jiska Classen. Two years after four days of being drilled on the Windows kernel in the same place, I came back, this time to learn iOS.
Official page: Practical iOS Reverse Engineering: App, Kernel & Firmware (OffensiveCon 2026)
This isn’t a technical write-up. It’s a first-hand account. I won’t go into the course material or the exercises, and I only describe the course as far as the syllabus on the official page does.
Why an iOS training
It started when my job required iOS kernel research. Starting iOS completely from zero on my own felt really hard, and right then I learned that OffensiveCon was running this training. The timing was perfect, so I signed up.
At the same OffensiveCon 2026, I also wanted to take “MalOpSec 2: EDR - The Great Escape” . But iOS research for work was the top priority, so I chose iOS.
In 2024 I paid for everything myself. This time the training was for work, so the company I do side work for covered the training fee and travel, and my main employer covered the hotel. And while in 2024 I went with two friends, this time I went alone.
Back in Berlin after two years
Via the UK, in a comfortable lounge
I flew via the UK. Thanks to my Amex Platinum card, I could use the lounge for first-class passengers during the layover there, which made the long transit genuinely comfortable.
Staying at the Hilton Berlin, and never leaving it
In 2024 I stayed at the hotel next to the venue; this time I stayed at the Hilton Berlin itself. My Amex Platinum came with Hilton Gold status, so I also got a room upgrade.
This year the trainings were held inside the Hilton Berlin, so my room and the classroom were in the same building. As a result, I never once left the Hilton Berlin during the stay.
Cost
Roughly:
| Item | Cost |
|---|---|
| Training | about ¥850,000 (listed on the official page as €4,800) |
| Travel | about ¥350,000 |
| Hotel | about ¥300,000 |
| Total | about ¥1,500,000 |
The total came to about ¥1,500,000, almost the same as in 2024.
No conference, but Pwn2Own
I didn’t attend the conference itself. Pwn2Own was running at the same time, though, so I watched how that was going.
What the course covers
The course works its way down the layers over four days: apps, then user-space internals, then the kernel, then firmware. According to the syllabus, the days break down like this:
- Day 1: iOS app fundamentals (static and dynamic analysis with Ghidra and Frida)
- Day 2: user-space internals (tracing execution, threads, an introduction to fuzzing)
- Day 3: where user space meets kernel space (XPC, Mach messages, IOKit, hardware-based protections)
- Day 4: firmware and advanced RE techniques (IOKit driver internals, co-processors, RTKit firmware)
The instructor, Jiska Classen, is a researcher known for reverse engineering wireless technology such as Bluetooth, UWB and AirTag. During the training you can borrow a jailbroken iPad for free, and you get the slides, exercises, solutions and cheat sheets. For the full curriculum, prerequisites and laptop requirements, see the official page .
The classroom
Panicking at the introductions
Day one started with introductions. Everyone in turn said why they had come to this training. As someone who can’t speak English at all, I honestly panicked.
The level of the attendees
The attendees didn’t seem quite as advanced as at WISE in 2024, where the room was full of people who held OSEE as a matter of course and were reporting kernel 0-days. Still, listening to the questions, several people clearly already had some experience attacking iOS.
I borrowed a device
I brought my own jailbroken iPhone for the exercises, but in the end I borrowed an iPad at the venue and used that.
How the four days went
Much easier to keep up than WISE
Compared with WISE, I could keep up far better this time. Some of that is probably my own skills improving over two years, but the bigger reason was that the course was designed to be kind to people starting from zero.
It started with an explanation of APIs using an app modeled on a real one, then covered how to use ipsw, how to get root access over SSH to a jailbroken device, and how to debug with Frida from there. Everything was explained very carefully, from the ground up.
I understood very little of the English
Once again, I could barely follow the spoken English. Even so, the course let even beginners make progress by doing the work with their own hands, so I came home with a lot.
No whisky time
In 2024 I joined the conversation at the whisky time after the training. This time I didn’t go once. Every day I went back to my room and rested.
After the training: what it did for my work
Back home, I use ipsw, which I learned in the training, to diff iOS before and after updates, and I have AI investigate those diffs. I’ve also been able to reproduce iOS exploits using vPhone.
I can’t say what I ultimately built, but for starting iOS research from zero, this training was a big shortcut. Five months later, I still rate it very highly.
For future attendees
- It’s ideal if you’re starting to learn iOS. It builds up carefully from the basics, so you won’t be left behind even if iOS is new to you.
- It may not run every year. If you want to take it, keep an eye on the OffensiveCon training list.
- Borrowing a device is easier. I brought my own, but with the instructor’s setup, questions get answered smoothly.
- You can take it without confident English. But there are introductions on day one, so prepare at least why you came, and you won’t panic.
Closing
I jumped into iOS because work demanded it, and this training cut a lot off the time it would have taken to start from zero. Even though I could barely follow the English, I came home with a lot from working through it hands-on. It was a good training.
At the venue I also got the usual OffensiveCon T-shirt and the OffensiveCon edition of Phrack.