credential-access

Active Directory

Responder and Internal Name-Resolution Poisoning

Disclaimer: This article is provided strictly for educational purposes and authorized security testing. Only run these t...
Cloud Security

Abusing AWS Instance Metadata (IMDS) and SSRF

Disclaimer: This article is provided strictly for educational purposes and authorized security testing. Only run these t...
Cloud Security

Cloud Credential Harvesting and Secret Sprawl

Disclaimer: This article is provided strictly for educational purposes and authorized security testing. Only run these t...
Cloud Security

Azure Storage Accounts and SAS Token Abuse

Disclaimer: This article is provided strictly for educational purposes and authorized security testing. Only run these t...
Active Directory

DCSync Attack and Defense: Abusing Directory Replication Rights

How DCSync abuses AD replication rights via DRSUAPI to dump credentials, and how blue teams can detect and stop it.
Windows Privesc

Practical Credential Theft with Mimikatz

A hands-on guide to dumping Windows credentials with Mimikatz and the LSA protections that stop it.
Windows Privesc

Dumping LSASS Memory: Techniques and Detection Evasion

A practical guide to dumping LSASS memory with comsvcs.dll, procdump, and nanodump, plus parsing with pypykatz and blue-team defenses.
Windows Privesc

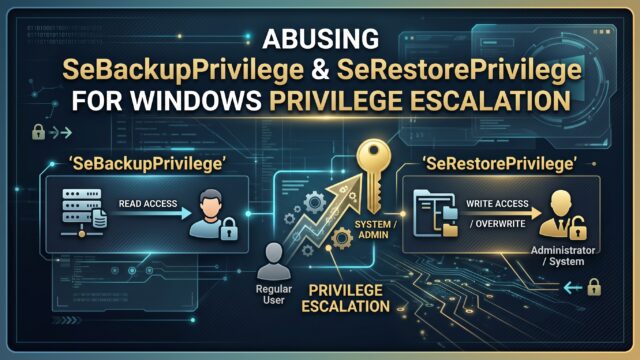
Abusing SeBackupPrivilege and SeRestorePrivilege for Windows Privilege Escalation

How attackers abuse SeBackupPrivilege/SeRestorePrivilege to dump SAM, SYSTEM, and ntds.dit, plus blue-team detection and defense.
Linux Privesc

SSH Key Hunting and Lateral Movement on Linux

Find SSH private keys, abuse authorized_keys and known_hosts, and pivot via agent forwarding across Linux hosts.
Linux Privesc

Credential Hunting on Linux: From .bash_history to Config Files

A practical guide to hunting cleartext credentials on Linux hosts via history files, config files, and grep, plus defenses.
Tools & Defense

Mastering the Impacket Suite: From Lateral Movement to Credential Extraction

A practical tour of Impacket's psexec, wmiexec, secretsdump, GetUserSPNs and smbserver, plus blue-team detection.
Cloud Security

Cloud Metadata Service (IMDS) Attacks via SSRF: Stealing Credentials and Defending IMDSv2

How attackers pivot from SSRF to cloud credential theft through 169.254.169.254, and how IMDSv2 and hop limits stop them.
Containers & DevSecOps

Secrets Management and Hunting Leaked Secrets in Git

Hunt leaked credentials in git history with gitleaks and trufflehog, then lock them down with HashiCorp Vault.